
INTRODUCTION
India has over 800 million internet users with one of the largest internet user base in the world1. In the last 10 years, online banking, online transactions, e-commerce, social media have become the reality of hundreds of millions of Indians. This digital adoption has been driven by government initiatives such as Digital India and Jan Dhan Yojana to rural and low-income communities that were not part of formal financial systems before2.
To a large extent, this is a true success story. The economic opportunity and convenience that the internet offers to the ordinary people are real. However, it has a serious drawback that has been mentioned in a lot less than the attention it deserves. With an increased number of individuals going online, with a large number of these individuals being first time users who have never been taught on how to identify an online threat, criminals have taken advantage to exploit them. In India, cybercrime is no longer a niche issue of a few victims that are technically advanced. It is a nationwide mass phenomenon, which affects common people.
According to the National Crime Records Bureau (NCRB) that collects and publishes crime statistics in annual Crime in India report, 27,248 cases of cybercrime were registered in 20183. By 2023, that number had risen to 86,420 a jump of 217 per cent in five years. During the same time, the crime rate (the number of cybercrimes per lakh of population) increased to 6.2 (initially it was 2.1). In 2023, there was the highest year on year increase in cybercrimes (31.2 per cent up) of any type of crime recorded by the NCRB compared to 20224.
Official NCRB case numbers just represent the tip of the iceberg. In 2024 alone, the government, through the National Cyber Crime Reporting Portal (NCRP), under the Ministry of Home Affairs, received more than 22.68 lakh (2.27 million) cybercrime complaints5. Citizens had complained of financial losses of Rs. 22,845 crores in 2018 to cyber fraud – almost Rs. 23,000 crores lost within one year6.
It is on this background of the skyrocketing cybercrime that the inefficiency of the legal system to put the offenders to justice has been wanting. Majority of cybercrime perpetrators of Indian citizens are never charged, not convicted and not penalized. The Information Technology Act, 2000 (IT Act) which is the main law dealing with cybercrime in India is more than 20 years old yet the conviction rate of cybercrime cases has not been above the low single digits out of all cases registered7. In 2021, 18 states and Union Territories in India had zero cybercrime convictions8. This is not merely a statistic of failure of enforcement. The backdrop of all unresolved cybercrime stories is a real victim: a farmer who lost his savings to a fraudulent investment opportunity, an elderly individual swindled by a digital arrest scam, a young woman whose personal photographs were stolen to blackmail her, a small business owner who had his bank account emptied. The magnitude of loss of finances in rupees. 7,465 crores in 2023 and Rs. 22,845 crores in 2024 shows how much harm is being done9. This gap is an attempt to comprehend this gap empirically in this paper. It poses the question: what does the official data really say about the situation with cybercrime and enforcement of the IT Act in India? It examines the statistics with attention- registration patterns, chargesheet rates, conviction rates, by state patterns and financial losses, and attempts to answer the question why enforcement has been so uniformly ineffective. The responses of the government and the conclusion of the paper with actual recommendations are also discussed.
This research discusses the data between 2018 and 2023, which is the entire range of data on NCRB that is published to date, and additional information on 2024 and early 2025 in the form of Parliamentary responses and government press releases10.
Research Gap
The literature on cybercrime in India is expanding, with a wealth of material on the text of the IT Act to the finer details of phishing and ransomware attacks. Other studies such as the 2023 report of Future Crime Research Foundation (FCRF) on cybercrime trends and the 2023 survey of the Internet Freedom Foundation on digital harassment have focused on certain aspects of the issue11.
Nevertheless, there is still a gap in the scholarly literature. Very few studies have collected the entire cascade of official empirical evidence of the number of complaints on the NCRP portal, to FIR registration, to chargesheet filing, to trial outcomes and conviction rates and correlated it to demonstrate precisely where and why the Indian system of enforcing cybercrime fails. Majority of the current literature is either doctrinal analysis of the provisions of the IT Act or a single facet of the issue (financial fraud or admissibility of digital evidence). The paper seals that gap by combining the information in the NCRB reports, Parliamentary responses, RBI reports and judicial ruling into a single, interrelated empirical image of cybercrime enforcement in India between 2018 and 202312.
Research Questions
This paper is guided by the following research questions:
1. What do official data sources reveal about the scale, nature, and growth of cybercrime in India between 2018 and 2023, and how wide is the gap between complaints and formal case registration?
2. What is the actual enforcement record under the IT Act, 2000 including chargesheet rates, conviction rates, and state-wise performance and what does this data reveal about the effectiveness of the law in practice?
3. What are the structural, legal, and institutional reasons for weak cybercrime enforcement in India, and what reforms are needed to make IT Act enforcement more effective?
Research Objectives
Aligned with the research questions above, this study has the following objectives:
• To compile and analyse year-wise cybercrime registration data, NCRP complaint statistics, and financial loss data from 2018 to 2024 using official government sources, in order to document the true scale of cybercrime in India and the reporting gap.
• To empirically examine chargesheet rates, conviction rates, and state-wise enforcement outcomes in cybercrime cases between 2017 and 2023, using NCRB data and MHA Parliamentary disclosures, and to assess how effective IT Act enforcement has been in practice.
• To identify the key structural and institutional barriers to effective cybercrime prosecution including forensic capacity, jurisdictional challenges, electronic evidence law, and trial delays and to formulate evidence-based policy recommendations.
Research Methodology
In this research paper, an empirical approach is employed. It is based on quantitative empirical evidence gathered through official government sources. This empirical data is systematically collected, organised and analysed.
Scope and Limitations
This paper has a limited scope, which is the enforcement history of the law of cybercrime in India during 2018-2023 based on the latest published data in the NCRB13. Where possible, 2024 and early 2025 data in Parliamentary replies and PIB statements are provided to present a more up-to-date image14. The article concentrates on the national level in India, and at the state level, on the largest states in terms of volume.
It should be admitted that the following limitations exist. To begin with, the official NCRB case statistics are grossly inaccurate with respect to the actual occurrence of cybercrime due to under-reporting. In a 2023 survey by Internet Freedom Foundation, approximately 68 per cent of victims in digital fraud do not report to the police largely because of a lack of confidence in the system, or awareness of reporting systems15. The official numbers that have been utilized in this paper thus are a low estimate of the entire picture.
Second, the data on conviction rates is not separated by individual type of offence in all years, thus, it is hard to compare the results in terms of enforcement of, say, the cases of fraud and the cases of stalking. Third, the Bharatiya Nagarik Suraksha Sanhita, 2023 (BNSS) and the Bharatiya Nyaya Sanhita, 2023 (BNS) supplanted the Indian Penal Code and the Code of Criminal Procedure, respectively, starting 1 July 202416. The reclassification of the data may indicate a discontinuity in the trend in the future.
THE LEGAL FRAMEWORK
The information technology Act, 2000.
The Information Technology Act, 2000 was India’s first comprehensive law to deal with cybercrime and electronic transactions17. It took effect on 17 June 2000 and was largely based on the UNCITRAL Model Law on Electronic Commerce; 199618. The Act was significantly revised in 2008 to cover a broader scope of cyber offences19. The revised edition of the IT Act is still the main law in the prosecution of cybercrime in India.
The following sections of the IT Act are the most crucial in the enforcement of cybercrime. Section 43 addresses the penalties related to unauthorised access to computer systems such as hacking and data theft20. Section 43A (added by the 2008 amendment) states that companies that deal with sensitive personal data have to ensure that they observe reasonable security practices and gives entitlement to compensation in case they do not21. Section 65 penalizes any person found guilty of tampering with computer code knowing of the act, with a jail time of up to three years or a fine of up to two lakh rupees or both22.
Section 66 will deal with computer related offences in general which will include acts such as hacking and data destruction as criminal offences and which are punishable with a sentence up to three years imprisonment23. Sections 66B to 66F are focused: Section 66C involves identity theft, Section 66D involves cheating through impersonation online, Section 66E involves the invasion of privacy and section 66F pertains to cyber terrorism, which carries a maximum penalty of life imprisonment24. Section 67, 67A and 67B address the issue of publishing obscene and child sexual abuse material electronically25.
In 2015, Shreya Singhal v. Union of India, the Supreme Court found the provision of Section 66A to have criminalised the offensive online communication as a violation of the right to free speech under Article 19(1)(a) of the Constitution of India26.
Other Relevant Laws.
Besides the principal Information Technology Act, 2000, there are some other significant legislations that have a supporting role in dealing with cybercrimes in India27. Such laws influence the protection of data, investigations and trials, and the presentation of evidence in court. Since this paper is devoted to the enforcement of the IT Act during the period of 2018-2023, it is helpful to learn about these new regulations and their links with the system of cybercrime prosecution in general.
The most significant new piece of cyberspace law in India in the recent past is the Digital Personal Data Protection Act, 2023 (DPDPA)28. This legislation imposes explicit obligations on businesses and organisations, which gather, store, or handle the personal data of common people. These organisations are called “data fiduciaries.” They are required to ensure that the data remains secure, they should only access it according to the reason why it was collected and they should bear the full responsibility in case of breach or leakage of such data under the DPDPA. It is directly applicable to cybercrime since most of the cases are related to theft or abuse of personal data. Victims can now claim compensation and the organisation can be fined in case a company does not do its duty. This law however is yet to be finalised on the ground with detailed rules being drafted as of April 2026. The Data Protection Board that the Act proposes to establish in order to address complaints and bring the rules to life is not fully functional yet.
Since 1 July 2024, two new significant laws substituted the previous Indian Penal Code and Code of Criminal Procedure. It was replaced by the Bharatiya Nagarik Suraksha Sanhita, 2023 (BNSS) instead of the Code of Criminal Procedure and the Bharatiya Nyaya Sanhita, 2023 (BNS) replaced the Indian Penal Code29. The BNS presents new clauses on the organised crime and terrorism. These provisions can occasionally be applicable in serious cybercrime cases – particularly where the fraud or assaults have been perpetrated by large criminal gangs or where national security is at stake30. The BNS is however not a special law developed strictly to deal with cybercrimes. It merely provides additional legal backing under some situations and not in place of the IT Act. As the period of the research article is 2018-2023, all information and analysis in the article is entirely old IPC and CrPC. The next reports after July 2024 can indicate a modification in the classification of cases due to these new laws31.
The other significant reform is the law of evidence. The Bharatiya Sakshya Adhiniyam, 2023 has replaced the old Indian Evidence Act. The old Evidence Act (65B) dealing with electronic records is now taken under 63 of the new Act32. This shift has been highly applicable in cases of cybercrimes since a majority of cases rely on digital evidence like emails, bank transaction records, and call logs and device evidence. The Supreme Court has already provided some clear directions on how such evidence should be certified; however, the new law seeks to streamline the process and make it more feasible to courts.
Lastly, there is a new Digital India Bill that the government is discussing which would fully substitute the IT Act, 2000 with new and more robust regulations to cope with the current digital realm33. This bill is supposed to address contemporary issues such as ransomware, deepfakes, crypto fraud, and dark-web crimes which are not entirely covered by the current IT Act. Yet, as of April 2026, the Digital India Bill remains yet to be presented in Parliament.
Key Gaps in the Law
The IT Act has several important gaps that make it hard to prosecute modern cybercrime. First, most of its crimes are relatively light punishments, two to three years of incarceration, which do not deter the organised networks of cybercrime offenders that can make crores of rupees through fraud. Second, the Act does not contain specifications on how police should investigate cyber offences, gather digital evidence, or data preservation. Third, it is silent on numerous types of cybercrime that have become prevalent since 2008, including ransomware, cryptocurrency-based fraud and dark web activities, as well as AI-generated deepfakes or morphed images.
CYBERCRIME REGISTRATION TRENDS (2018–2023)
The Year-by-Year Picture
Table 1 below sets out the complete year-wise data on registered cybercrime cases in India from 2018 to 2023. This data is drawn from NCRB’s Crime in India reports for each of the six years34.
Table 1: Registered Cybercrime Cases in India (2018–2023)
| Year | Cases Registered | Year-on-Year Change (%) | Crime Rate (per lakh population) |
|---|---|---|---|
| 2018 | 27,248 | — | 2.1 |
| 2019 | 44,735 | +64.2% | 3.3 |
| 2020 | 50,035 | +11.8% | 3.7 |
| 2021 | 52,974 | +5.9% | 3.9 |
| 2022 | 65,893 | +24.4% | 4.8 |
| 2023 | 86,420 | +31.2% | 6.2 |
Source- NCRB, Crime in India Reports 2018-2023, Ministry of Home Affairs, Government of India35.
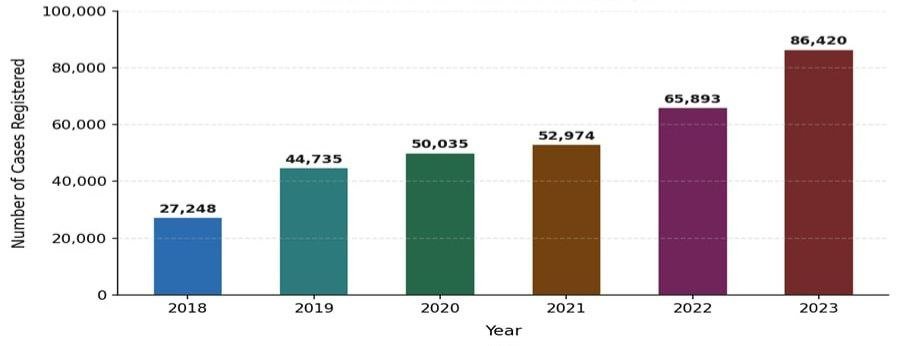
Figure 1: Registered Cybercrime Cases in India (2018–2023). Source: NCRB, Crime in India Reports36.
The above data has a distinct and steady increasing pattern. The number of cases increased more than threefold in 2018-2023. The greatest increase was between 2018 and 2019, 64.2 per cent, which is due in part to the rapid growth in the use of digital payments since demonetisation in 2016 and the fast growth of UPI37. Millions of individuals who had never previously engaged in digital finance went online within an extremely short period of time, and most of them were not aware of the risks of fraud that it presented.
The two years 2020 and 2021 are the years of the pandemic, and their growth rates are relatively lower38. This is probably not the case because cybercrime actually decreased during the pandemic – in reality, there was a significant increase in online activity during lockdowns – but due to a limited physical access to police departments, and a large proportion of victims might not have made formal complaints. The current rapid growth in 2022 and 2023 indicates not only real growth but also a potentially improved reporting39.
In the NCRB 2023 report, it is also observed that IT Act offenses particularly increased by 36 per cent in 2023 that is, a higher rate than 31.2 per cent increase in cybercrime as a whole, indicating that technological crimes are rising even more rapidly than the overall trend40.
The Reporting Gap
The NCRB case numbers discussed above are formal FIRs cases registered by police. The actual incidence of cybercrime is far higher. The National Cyber Crime Reporting Portal (NCRP), set up in 2019 under I4C, is a platform where citizens can report cybercrimes online. The complaint volumes on this portal tell a very different story.
Table 2: NCRP Complaints vs. Registered FIRs (2021–2024)
| Year | NCRP Complaints (in lakh) | NCRB Registered Cases | Approx. Conversion to FIR |
|---|---|---|---|
| 2021 | 4.52 lakh | 52,974 | ~11.7% |
| 2022 | 10.29 lakh | 65,893 | ~6.4% |
| 2023 | 15.96 lakh | 86,420 | ~5.4% |
| 2024 | 22.68 lakh | Data awaited | ~3.8% (est.) |
Source: MHA Parliamentary Reply, December 2025; NCRB Crime in India Reports 2021-2023.
About 1.6 million complaints were received via the NCRP portal between January 2020 and December 2022, of which only around 32,000 (or about 2 per cent) were turned into formal police cases41. By 2024, the NCRP was getting 22.68 lakh complaints annually, but the rate of converting FIR remained at an underestimated 4 per cent42. It is an impressive institutional failure: of all cybercrime cases that citizens take the time to report them to the authorities, nearly all do not receive the formal pick-up to be properly investigated.
NATURE AND CATEGORIES OF CYBERCRIME
The NCRB 2023 report breaks down cybercrime cases by the motive of the offender. This is useful because it shows what kind of crimes are actually being committed, and therefore what kinds of enforcement capacity are most needed43.
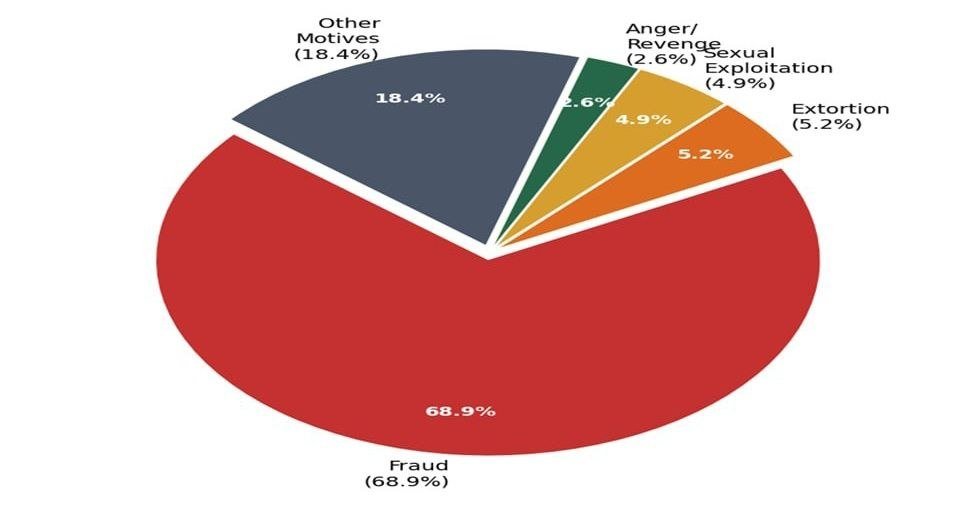
Figure 2: Motive-wise Distribution of Cybercrime Cases in India (2023). Total = 86,420 cases. Source: NCRB, Crime in India 202344
Financial fraud, as Figure 2 indicates, is by far the most prevalent reason of cybercrime in India. In 2023, fraud accounted for 59,526 cases about 68.9 per cent of the total45. In 4,526 cases (5.2 per cent) the motive was extortion and in 4,199 cases (4.9 per cent) the motive was sexual exploitation46. Cases that were influenced by anger or personal revenge included 2,228 cases (2.6 per cent). The rest of the 18.4 per cent was composed of a huge variety of other motives47.
In the financial fraud category, UPI-related fraud and internet banking fraud, according to a study commissioned by the Future Crime Research Foundation (FCRF), an incubator organisation within IIT Kanpur, constituted nearly half of all cybercrime cases between 2020 and 2023, highlighting how the thriving digital payments ecosystem in India has become a lucrative target by cybercriminals in 202348.
Other interesting sub-categories of the 2023 NCRB data are: circulation of sexually explicit material (2,168 cases), child sexual abuse material (1,472 cases), cyberbullying and stalking of women and children (1,305 cases), and fake news spread on social media (209 cases)49. Women-related crimes in and through cyber avenues topped 19,000 cases in 2023 compared to approximately 6,000 in 201850. In 2023, crimes involving victims were almost 2,000, as compared to slightly more than 230 in 201851.
THE ENFORCEMENT GAP: CHARGESHEETS AND CONVICTIONS
Chargesheet Rates
The document submitted to a court by the police to initiate the trial process is known as a chargesheet when an investigation is conducted. The rate of chargesheet, which is the proportion of registered cases that lead to a chargesheet, is a simple indicator of the thoroughness with which the cases are being investigated. This rate has continued to be low in the cases of cybercrime. The 2022 national rate of charge sheeting cybercrime was 29.6 per cent, or, to put it another way, in every 100 FIRs, it was possible to complete the investigation and file chargesheets in about 30 cases52. Delhi was at an outlier of 89.3 per cent, whereas most states were much lower53. As of 2023, the total chargesheet rate has dropped even further to about 22 per cent54.
Conviction Data (2017–2023)
The table 3 below gives the fullest available image of cybercrime convictions in India basing on the data provided by the Ministry of Home Affairs in a reply in Parliament in December 2025, with previous data revealed in 202255.
Table 3: Cybercrime Chargesheets Filed vs. Convictions Secured (2017–2023)
| Year | Cases Registered | Chargesheets Filed | Convictions | Rate (% of Chargesheets) |
|---|---|---|---|---|
| 2017 | 21,796 | 5,180 | 152 | 2.9% |
| 2018 | 27,248 | 7,000 | 490 | 7.0% |
| 2019 | 44,735 | 9,000 | 360 | 4.0% |
| 2020 | 50,035 | 14,087 | 1,109 | 7.9% |
| 2021 | 52,974 | 18,000+ | 490 | 2.7% |
| 2022 | 65,893 | ~19,500 | 886 | 4.5% |
| 2023 | 86,420 | ~19,000 | 886* | <3% (of trials) |
Source: MHA, Lok Sabha Reply No. 452 (Dec. 2, 2025); The Print (Dec. 2022); NCRB Crime in India 2023. 2023 convictions include cases pending from earlier years56.
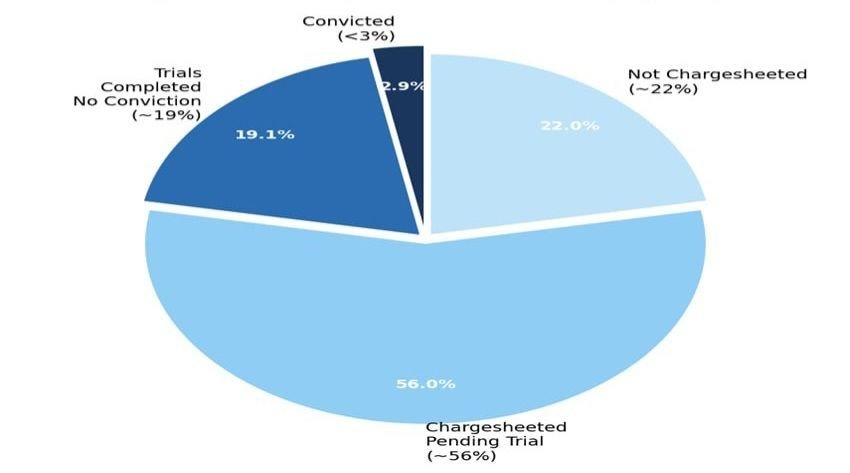
Figure 3: The Cybercrime Enforcement Pyramid (2023) as percentage of registered cases. Source: NCRB 2023; CJP Report 202557.
The combination of Figure 3 and Table 3 paints a very worrying picture. Out of all the 100 cybercrime FIRs that were registered in 2023, 22 had a chargesheet58. Among the ones that were put on trial, less than 3 per cent were found guilty59. That is, when you file a cybercrime complaint with the police, there is a better than 1 in 30 probability that the criminal will end up being convicted.
STATE-WISE DISTRIBUTION OF CYBERCRIME
Cybercrime in India is geographically concentrated. In 2023, just three states Karnataka, Telangana, and Uttar Pradesh together accounted for 59.5 per cent of the national total of 86,420 registered cases60. Table 4 below sets out the data for major states.
Table 4: State-wise Cybercrime Data, 2023 Select States
| State | Cases Registered (2023) | Crime Rate (per lakh) | Chargesheet Rate (approx.) | Notable Feature |
|---|---|---|---|---|
| Karnataka | 21,889 | 32.3 | 18.1% | Highest absolute case volume nationally |
| Telangana | 18,236 | 47.0 | 20.9% | Highest crime rate nationally; 98 of 209 fake news cases |
| Uttar Pradesh | 10,794 | 4.6 | ~35% | Highest convictions in 2021 (292 cases) |
| Maharashtra | 6,399 | 5.1 | ~22% | Highest sexual exploitation cases |
| Rajasthan | 5,625 | 7.1 | ~28% | Major fraud hub; high rural victimisation |
| Mizoram | Low | — | 100% | 100% chargesheet rate (small absolute base) |
Source: NCRB, Crime in India 2023; MHA Parliamentary Reply, December 202561.
Both Karnataka and Telangana are significant hubs of Indian technology and IT services sector. Their numbers in cybercrime are also partly due to increased digital penetration – there are more people online which translates to more people who can be targeted. Nonetheless, they also indicate the existence of improved reporting infrastructure. Cyber police stations at state level in both states are more advanced as compared to most other locations in India. An example is Bengaluru city where more cases of cybercrime have been reported in 2023 than in several states.
States with low internet penetration and poor police infrastructure (in the north and central regions of India) record fewer cases of cybercrime. But this is almost certainly under-reporting as opposed to actual decreased crime. The rural and semi-urban populations in these states are typically more susceptible to some forms of scam – e.g. counterfeit employment opportunities, counterfeit agricultural credit schemes, and lottery fraud – that take advantage of decreased digital literacy.
THE FINANCIAL COST OF CYBERCRIME
In a response to Lok Sabha in December 2025, the Ministry of Home Affairs released detailed information on the financial losses caused by cybercrimes62. The statistics indicate a phenomenal and accelerated increase.
Table 5: Financial Losses from Cybercrime/Cyber Fraud in India (2022–2024)
| Year | Financial Loss Reported (Rs. Crore) | NCRP Complaints (lakh) | Approx. Loss per Complaint |
|---|---|---|---|
| 2022 | Rs. 2,290.24 crore | 10.29 lakh | Rs. 2,225 |
| 2023 | Rs. 7,465.18 crore | 15.96 lakh | Rs. 4,678 |
| 2024 | Rs. 22,845.73 crore | 22.68 lakh | Rs. 10,073 |
Source: MHA, Lok Sabha Reply, December 2025. Data from NCRP and CFCFRMS combined63
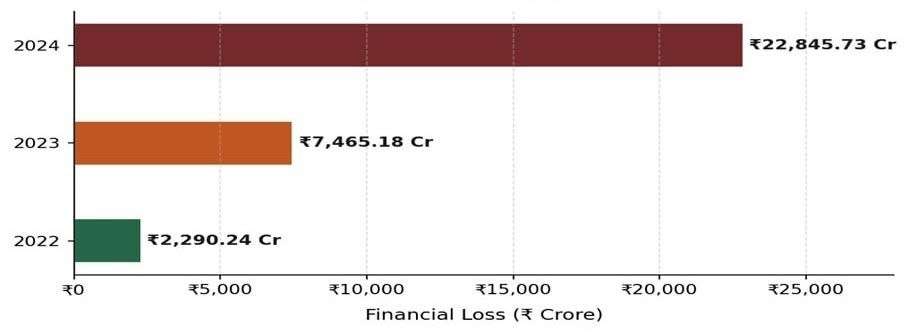
Figure 4: Financial Losses from Cybercrime in India (2022–2024). Source: MHA, Lok Sabha Reply, December 202564.
The economic damage that was inflicted by cybercrime increased by Rs. 2,290 crores in 2022 to Rs. 22,845 crores in 2024 – almost ten times more in two years65. In perspective: the 2024 figure is compared with the 2025-26 Union Budget: it was only around Rs. 782 crores on cybersecurity – less than 4 per cent of what was lost by citizens to cybercriminals in that very year alone66.
The additional information on digital payment fraud can be found in the Annual Report 2023-24 of the Reserve Bank of India67. There were 29,082 cases of card and internet banking frauds recorded by RBI in terms of value of Rs. 1 lakh or more in 2023-24, totalling Rs. 1,457 crores68. Since 2020-21, frauds of over Rs. in digital payments. 1 lakh has increased 11 times and 12 times in value and number respectively69.
The so-called digital arrest scam is among the most rapidly developing new groups. In this form of fraud, the criminals imitate the role of CBI officers, customs officials, or TRAI representatives, and call the victims on video, telling them that they are being arrested due to some crime under the digital arrest. Then they blackmail huge sums of money to clear the case. No concept of a digital arrest exists in Indian law, any actual arrest should be accomplished through an actual legal procedure, but millions of citizens are ignorant of the fact. In 2022, the NCRP documented 39,925 of such incidents and reported 1,23,672 in 2024, with reported losses increasing by Rs. 91 crores in 2022 to Rs. 1,935 crores in 202470
WHY ENFORCEMENT BREAKS DOWN: THE MAIN CHALLENGES.
A. Weak Digital Forensics.
Robust digital pieces of evidence, such as IP logs, transactions, device logs, metadata, are crucial to the prosecution of cybercrime. It is, therefore, necessary to have trained forensic analysts to collect, preserve and present this evidence in a court of law. Such analysts are not available in most district police stations in India. The upshot is that in many instances where a cybercrime has been registered and even investigated, the evidence collected is so often insufficient to support a prosecution in court.
Section 65B of the Indian Evidence Act (now Section 63 of the Bharatiya Sakshya Adhiniyam, 2023) on the admissibility of electronic evidence has been a longstanding issue also71. In Arjun Panditrao Khotkar v. Kailash Kushanrao Gorantyal (2020), the Supreme Court provided clarity regarding the regulations on electronic evidence certificates, although adherence to them in the district courts is rather uneven and inconsistent72.
B. Cross-Border Crime
Much of the cybercrime against Indian citizens is coordinated and carried out overseas – especially in Southeast Asian nations such as Myanmar, Cambodia and Vietnam where organised fraud groups run extensive activities. The Indian law enforcement lacks jurisdiction over individuals that are in other countries. There are Mutual Legal Assistance Treaties (MLATs) with most of these nations on paper, but are slow and bureaucratically challenging to operationalize.
C. Police Capacity Constraints
Even prior to the cybercrime explosion, the police force in India was already grossly understaffed as compared to the population. The state and district level cybercrime units are inadequately staffed, trained and are overwhelmed by complaints. In the years 2020-2022, the NCRP was able to receive approximately 1.6 million complaints, out of which 32,000 (2 per cent) were turned into FIRs73. This is not due to the fact that the rest of the complaints were all false- it is just that there is not enough police time to investigate all the complaints.
D. Under-Reporting
In India, a survey by the Internet Freedom Foundation (2023) revealed that approximately 68 per cent of individuals who fell victims to some form of digital fraud or online harassment never reported the incident to police74. The primary causes were: no expectation that the police would respond, fear of embarrassment and stigma, and lack of knowledge of where and how to report. It implies that the bureaucratic crime rates are huge, but this only reflects a small part of what is really going on.
E. Court Delays and Trial Pendency.
Cybercrime cases travel slowly through the courts even in places where there are chargesheets and trials are commenced. The judicial system in India has massive backlogs of all forms of crime. Even the cases of cybercrimes involve expert testifying and technical evidence and this also introduces delays. Criminal cases may take years to be resolved, and in the meantime, the digital data can be lost or become outdated, and witnesses can be unavailable.
GOVERNMENT RESPONSE
The federal government has made a number of initiatives in order to deal with the increase in cybercrime in the last couple of years. On 1 July 2024, the Indian Cyber Crime Coordination Centre (I4C) was finally organized as an attached office under the MHA75. The National Cyber Crime Reporting Portal (NCRP) offers citizens with a web-based platform in reporting any form of cybercrime76. The fraud victims are provided with the toll-free helpline number 1930, which enables them to report instantly and request to freeze the transactions before transfer of the money outside the country77.
Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS) is an online system that notifies banks to freeze accounts that receive fraudulent transfers78. It had saved more than Rs by early 2025. On 1.4 million complaints, 4,386 crores, and prevented in 2024 alone79 Rs. 5,489 crores as a result of reaching criminals. It has also blocked 9,42 lakh SIM cards and 2,63,348 IMEIs associated with cyber fraud by the government80. In September 2024, the Suspect Registry was implemented, which identified 24.67 lakh suspected mule accounts, stopping Rs. 8,031 crores in transactions81.
The cyber threat advisories issued by CERT-In (Indian Computer Emergency Response Team) established under Section 70B of the IT Act, as well as the requirement of security audits of critical organisations, are mandatory82. The budget of 2025-26 by the Union Budget was in the form of Rs. 782 crores on cybersecurity infrastructure83. The PratiBimb geospatial mapping application, created to serve state police, has assisted in locating regions of cybercrime activity and resulted in 16,840 suspects being arrested by early 202584.
These are real and substantial measures. And not yet are they enough. Financial losses continue to increase at a higher rate than the government is responding. The court record on enforcement- the actual conviction rate has not significantly improved. A majority of the complaints remain unexamined. What has been so far is more about symptoms rather than root causes.
RECOMMENDATIONS
According to the empirical results of this paper, the six following recommendations are provided:
1. Enact a New, Comprehensive Cybercrime Law.
The IT Act, 2000 is more than 20 years old and has failed to keep pace with the contemporary cybercrime85. India requires its own Cybercrime Act, specific to the ransomware problem, cryptocurrency fraud, and digital arrest scams, deepfakes generated by artificial intelligence, and crimes perpetrated on dark webs. Digital India Bill should be presented in Parliament immediately, and its significant consultation with law enforcement, civil society, and technological professionals should occur.
2. Develop Digital Forensic Capacity on the District Level.
Digital forensic analysts should be deployed to every district in India at least by having one trained digital forensic analyst attached to the police. State forensic science laboratories should be updated to deal with new evidence of cybercrime. States that do not have the budget to do so should be provided with central funds. Investigators and prosecutors who handle digital evidence should be trained on the same and it should be regular.
3. Establish Special Cybercrime Courts.
Each state should have fast-track courts that deal solely with cybercrime cases. The operation of these courts should have time limits as set by statute within which a trial must be concluded, e.g. within 12 months of chargesheet being filed. Specialised training in IT law, digital evidence and technical aspects of cyber offences at the National Judicial Academy is required of judges who are appointed to such courts.
4. Fix the FIR Conversion Rate
The present level of converting NCRP complaints to FIRs is too low. The state governments must be made to establish minimum targets of FIR conversion and report the same to MHA. At the level of sub-division, or the district level, special Cybercrime Investigation Units should be created, equipped, staffed, and trained.
5. Strengthen International Cooperation.
Given that much of the cybercrime in which the Indian citizens fall prey is committed by foreign nations, India needs to immediately revise its Mutual Legal Assistance Treaties (MLATs) with the major countries, especially the Southeast Asian countries, and agree on expedited mechanisms of sharing evidence and extraditing suspects. India should also enhance its liaison position with the INTERPOL86 cybercrime unit and seek a speedier time-table on the proposed UN Cybercrime Convention.
6. Establish a National Cyber Literacy Mission.
India ought to conduct an extended, nationwide campaign to inform ordinary people on the prevalent cybercrime techniques, reporting of such cases, and simple skills on digital safety. This campaign, as big as the financial literacy programmes of RBI, must be conducted in all the major regional languages and must directly approach rural masses, the old and elderly, women, and individuals who have not yet been introduced to internet.
CONCLUSION
The facts discussed in this paper are obvious: cybercrime in India is increasing at such a fast rate, and the law enforcement system in the country is lagging. The number of registered cases increased more than threefold in 2018-2387. Citizens lost Rs. 22,845 crores to cybercriminals in 202488. In 2024 alone, more than 22 lakh complaints were registered on the NCRP portal – but of those that were turned into formal police cases, less than 4 per cent were convicted89.
As a time-appropriate law, the IT Act, 2000 came in handy, but it is no longer applicable in 2010 in a country that handles billions of digital transactions every month90. Enforcement gap is not caused by a single issue but as a combination of many factors, such as poor forensics, jurisdictional restrictions, police manpower shortages, slow court system, and millions of citizens who have never been educated on how they can protect themselves on the Internet.
All these issues are not going to be solved fast and inexpensively. But they have to be dealt with. The picture of the cost of inaction is highly evident in the empirical evidence that has been compiled in this paper. With each year, which goes by without any serious reform, cybercriminals become more audacious and their means more advanced, and the scope of their victims expands. The desire of India to become one of the most prosperous digital economies is impossible to achieve when people are not able to believe that their money, their data, and their dignity are secured when they log in.
*****
Footnotes
1. Telecom Regulatory Authority of India, The Indian Telecom Services Performance Indicators (2023).
2. Press Information Bureau, Govt. of India, Pradhan Mantri Jan Dhan Yojana (PMJDY) (Aug. 2023).
3. National Crime Records Bureau, Crime in India 2018 (2020).
4. National Crime Records Bureau, Crime in India 2023 (2025).
5. Ministry of Home Affairs, Govt. of India, National Cyber Crime Reporting Portal Data (Parliamentary Reply, 2024).
6. Ministry of Home Affairs, Govt. of India, Cyber Crime Complaints and Financial Losses Reported on NCRP (2024).
7. Information Technology Act, No. 21 of 2000, India Code (2000).
8. National Crime Records Bureau, Crime in India 2021 (2023), https://ncrb.gov.in.
9. Lok Sabha Unstarred Question No. 2396, Ministry of Home Affairs, Govt. of India (Dec. 12, 2023) (reporting cyber fraud losses via NCRP); Press Information Bureau, Govt. of India, Cyber Fraud Losses and Complaints Data (2024).
10. Ministry of Home Affairs, Govt. of India, Annual Report 2023–24; Lok Sabha & Rajya Sabha Debates and Unstarred Questions (2024–2025).
11. Future Crime Research Foundation, Cybercrime in India Report 2023 (2023), https://www.futurecrime.org; Internet Freedom Foundation, Online Harassment and Digital Rights in India: Survey Report 2023 (2023).
12. National Crime Records Bureau, Crime in India (2018–2023) (various years); Reserve Bank of India, Annual Report 2022–23; Lok Sabha Unstarred Questions, Ministry of Home Affairs, Govt. of India (2023–2025), https://loksabha.nic.in; Anvar P.V. v. P.K. Basheer, (2014) 10 S.C.C. 473 (India)
13. National Crime Records Bureau, Crime in India (2018–2023) (various years).
14. Ministry of Home Affairs, Govt. of India, Annual Report 2023–24; Press Information Bureau, Govt. of India, Cyber Crime Data Releases (2024–2025).
15. Internet Freedom Foundation, Digital Fraud and Online Harassment Survey Report 2023 (2023).
16. Bharatiya Nagarik Suraksha Sanhita, No. 46 of 2023, § 1(2) (India); Bharatiya Nyaya Sanhita, No. 45 of 2023, § 1(2) (India); Ministry of Home Affairs, Govt. of India, Implementation of New Criminal Laws (2024).
17. Information Technology Act, No. 21 of 2000, pmbl., India Code (2000).
18. U.N. Comm’n on Int’l Trade Law (UNCITRAL), Model Law on Electronic Commerce (1996).
19. Information Technology (Amendment) Act, No. 10 of 2009, India Code (2009)
20. Information Technology Act, No. 21 of 2000, § 43, India Code (2000).
21. Id. § 43A.
22. Id. § 65
23. Id. § 66
24. Id. §§ 66B–66F
25. Id. §§ 67–67B.
26. Shreya Singhal v. Union of India, (2015) 5 S.C.C. 1 (India).
27. Information Technology Act, No. 21 of 2000, India Code (2000).
28. Digital Personal Data Protection Act, No. 22 of 2023, India Code (2023).
29. Bharatiya Nyaya Sanhita, No. 45 of 2023, § 1(2) (India); Bharatiya Nagarik Suraksha Sanhita, No. 46 of 2023, § 1(2) (India).
30. Bharatiya Nyaya Sanhita, No. 45 of 2023, chs. on organized crime & terrorism (India).
31. Indian Penal Code, No. 45 of 1860, India Code (1860); Code of Criminal Procedure, No. 2 of 1974, India Code (1974).
32. Id. § 63; Indian Evidence Act, No. 1 of 1872, § 65B (India).
33. Ministry of Electronics & Information Technology, Govt. of India, Consultation Paper on Digital India Act (2023).
34. National Crime Records Bureau, Crime in India (2018–2023).
35. Id.
36. National Crime Records Bureau, Crime in India (2018–2023) (various years).
37. Reserve Bank of India, Annual Report 2019–20; Press Information Bureau, Govt. of India, Growth of Digital Payments in India (2020).
38. World Health Organization, COVID-19 Pandemic Timeline (2020–2021).
39. National Crime Records Bureau, Crime in India 2022 (2024).
40. National Crime Records Bureau, Crime in India 2023 (2025).
41. Ministry of Home Affairs, Govt. of India, NCRP Complaints Data (Parliamentary Reply, 2023–2024).
42. Lok Sabha Unstarred Question No. 2396, Ministry of Home Affairs, Govt. of India (Dec. 12, 2023).
43. National Crime Records Bureau, Crime in India 2023 (2025).
44. Id.
45. Id.
46. Id.
47. Id.
48. Future Crime Research Foundation, Cybercrime in India Report 2023 (2023), https://www.futurecrime.org
49. National Crime Records Bureau, Crime in India 2023 (2025).
50. National Crime Records Bureau, Crime in India (2018 & 2023) (various years).
51. Id.
52. National Crime Records Bureau, Crime in India (2022) (2024).
53. Id.
54. National Crime Records Bureau, Crime in India 2023 (2025).
55. Ministry of Home Affairs, Govt. of India, Lok Sabha Unstarred Question No. 452 (Dec. 2, 2025); National Crime Records Bureau, Crime in India (2017–2023) (various years).
56. Id.; The Print, Explained: India’s Rising Cybercrime and Low Conviction Rates (Dec. 2022).
57. National Crime Records Bureau, Crime in India 2023 (2025); Citizens for Justice & Peace, Cybercrime Enforcement Report (2025).
58. National Crime Records Bureau, Crime in India 2023 (2025).
59. Ministry of Home Affairs, Govt. of India, Lok Sabha Unstarred Question No. 452 (Dec. 2, 2025).
60. National Crime Records Bureau, Crime in India 2023 (2025).
61. Id.; Ministry of Home Affairs, Govt. of India, Lok Sabha Unstarred Question No. ___ (Dec. 2025).
62. Id.
63. Id.
64. Id.
65. Ministry of Home Affairs, Govt. of India, Lok Sabha Unstarred Question No. ___ (Dec. 2025), https://loksabha.nic.in
66. Ministry of Finance, Govt. of India, Union Budget 2025–26 (Expenditure Profile).
67. Reserve Bank of India, Annual Report 2023–24 (2024).
68. Id.
69. Id.
70. Ministry of Home Affairs, Govt. of India, Lok Sabha Unstarred Question No. ___ (Dec. 2025).
71. Indian Evidence Act, No. 1 of 1872, § 65B (India); Bharatiya Sakshya Adhiniyam, No. 47 of 2023, § 63 (India).
72. Arjun Panditrao Khotkar v. Kailash Kushanrao Gorantyal, (2020) 7 S.C.C. 1 (India).
73. Ministry of Home Affairs, Govt. of India, NCRP Data (Parliamentary Reply 2023–2024).
74. Internet Freedom Foundation, Digital Fraud & Online Harassment Survey 2023.
75. Ministry of Home Affairs, Govt. of India, Indian Cyber Crime Coordination Centre (I4C).
76. National Cyber Crime Reporting Portal.
77. Ministry of Home Affairs, Govt. of India, Helpline 1930 for Cyber Fraud.
78. Ministry of Home Affairs, Govt. of India, CFCFRMS Framework (2024)
79. Ministry of Home Affairs, Govt. of India, Lok Sabha Unstarred Question No. ___ (2025) (data on CFCFRMS recoveries and complaints), https://loksabha.nic.in.
80. Id.
81. Ministry of Home Affairs, Govt. of India, Cybercrime Prevention Initiatives & Suspect Registry Data (2024–2025).
82. Information Technology Act, No. 21 of 2000, § 70B, India Code (2000); Indian Computer Emergency Response Team (CERT-In), Govt. of India, Cyber Security Directions (2022).
83. Ministry of Finance, Govt. of India, Union Budget 2025–26 (Expenditure Profile).
84. Ministry of Home Affairs, Govt. of India, Pratibimb Platform Overview & Cybercrime Tracking Data (2025).
85. Information Technology Act, No. 21 of 2000, India Code (2000).
86. Ministry of External Affairs, Govt. of India, Mutual Legal Assistance Treaties, https://mea.gov.in; INTERPOL, Cybercrime Directorate Overview.
87. National Crime Records Bureau, Crime in India (2018–2023) (various years).
88. Ministry of Home Affairs, Govt. of India, Lok Sabha Unstarred Question No. ___ (Dec. 2025).
89. Id
90. Information Technology Act, No. 21 of 2000, India Code (2000).